What is confidential computing?
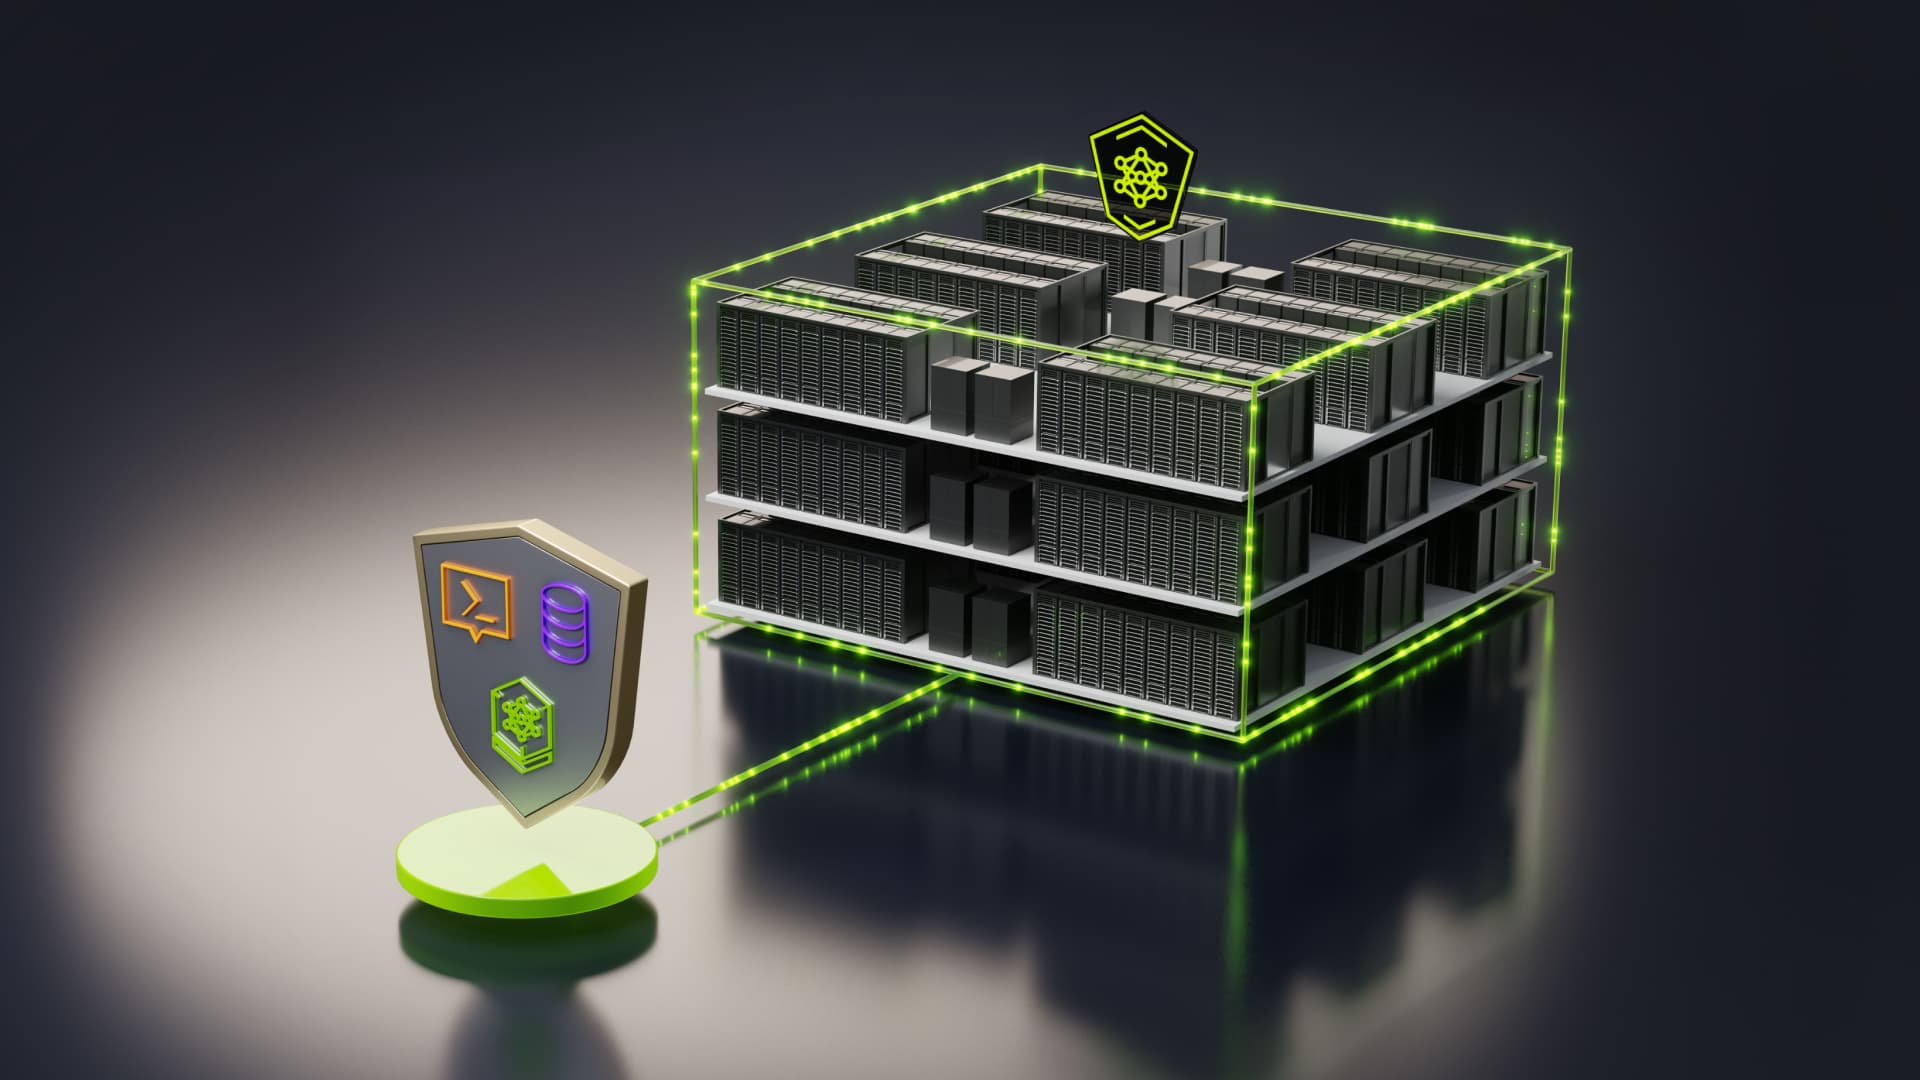
NVIDIA's confidential computing layer isolates AI models and data at the hardware level while they run. The company expanded that layer today with a new deployment option called Confidential Bare Metal.
The option lets frontier model builders run sensitive workloads on third-party cloud, neocloud and enterprise infrastructure while retaining control of their models and data. Builders can own and operate their own software stacks, including host and platform infrastructure software.
Three deployment options
NVIDIA now offers confidential computing under a single security architecture with three options:
- Confidential Bare Metal: For bare-metal infrastructure
- Confidential Containers: For Kubernetes environments
- Confidential Virtual Machines: For virtualized environments
The company is also introducing new platform security controls to protect data in transit, measure platform integrity and enforce hardware-level access restrictions.
Who is backing it?
Cohere plans to integrate Confidential Bare Metal into Cohere Model Vault. Google Cloud will extend support to A4X Max instances powered by NVIDIA GB300 NVL72 systems.
CoreWeave, Firmus, GMI Cloud, Google Cloud, IREN, Lambda, Microsoft Azure Infrastructure, Nebius, Nscale and Vultr said they support NVIDIA Confidential Computing deployments. Systems partners include Cisco, Dell Technologies and HPE.
Hardware coverage
Support now extends to NVIDIA Grace Blackwell NVL72, bringing confidential computing to rack-scale systems, as well as x86-based NVIDIA HGX Rubin NVL8 and NVIDIA DGX Rubin NVL8 systems. NVIDIA says the offering will also integrate with NVIDIA DSX OS as a reference architecture for cloud providers.