What happened
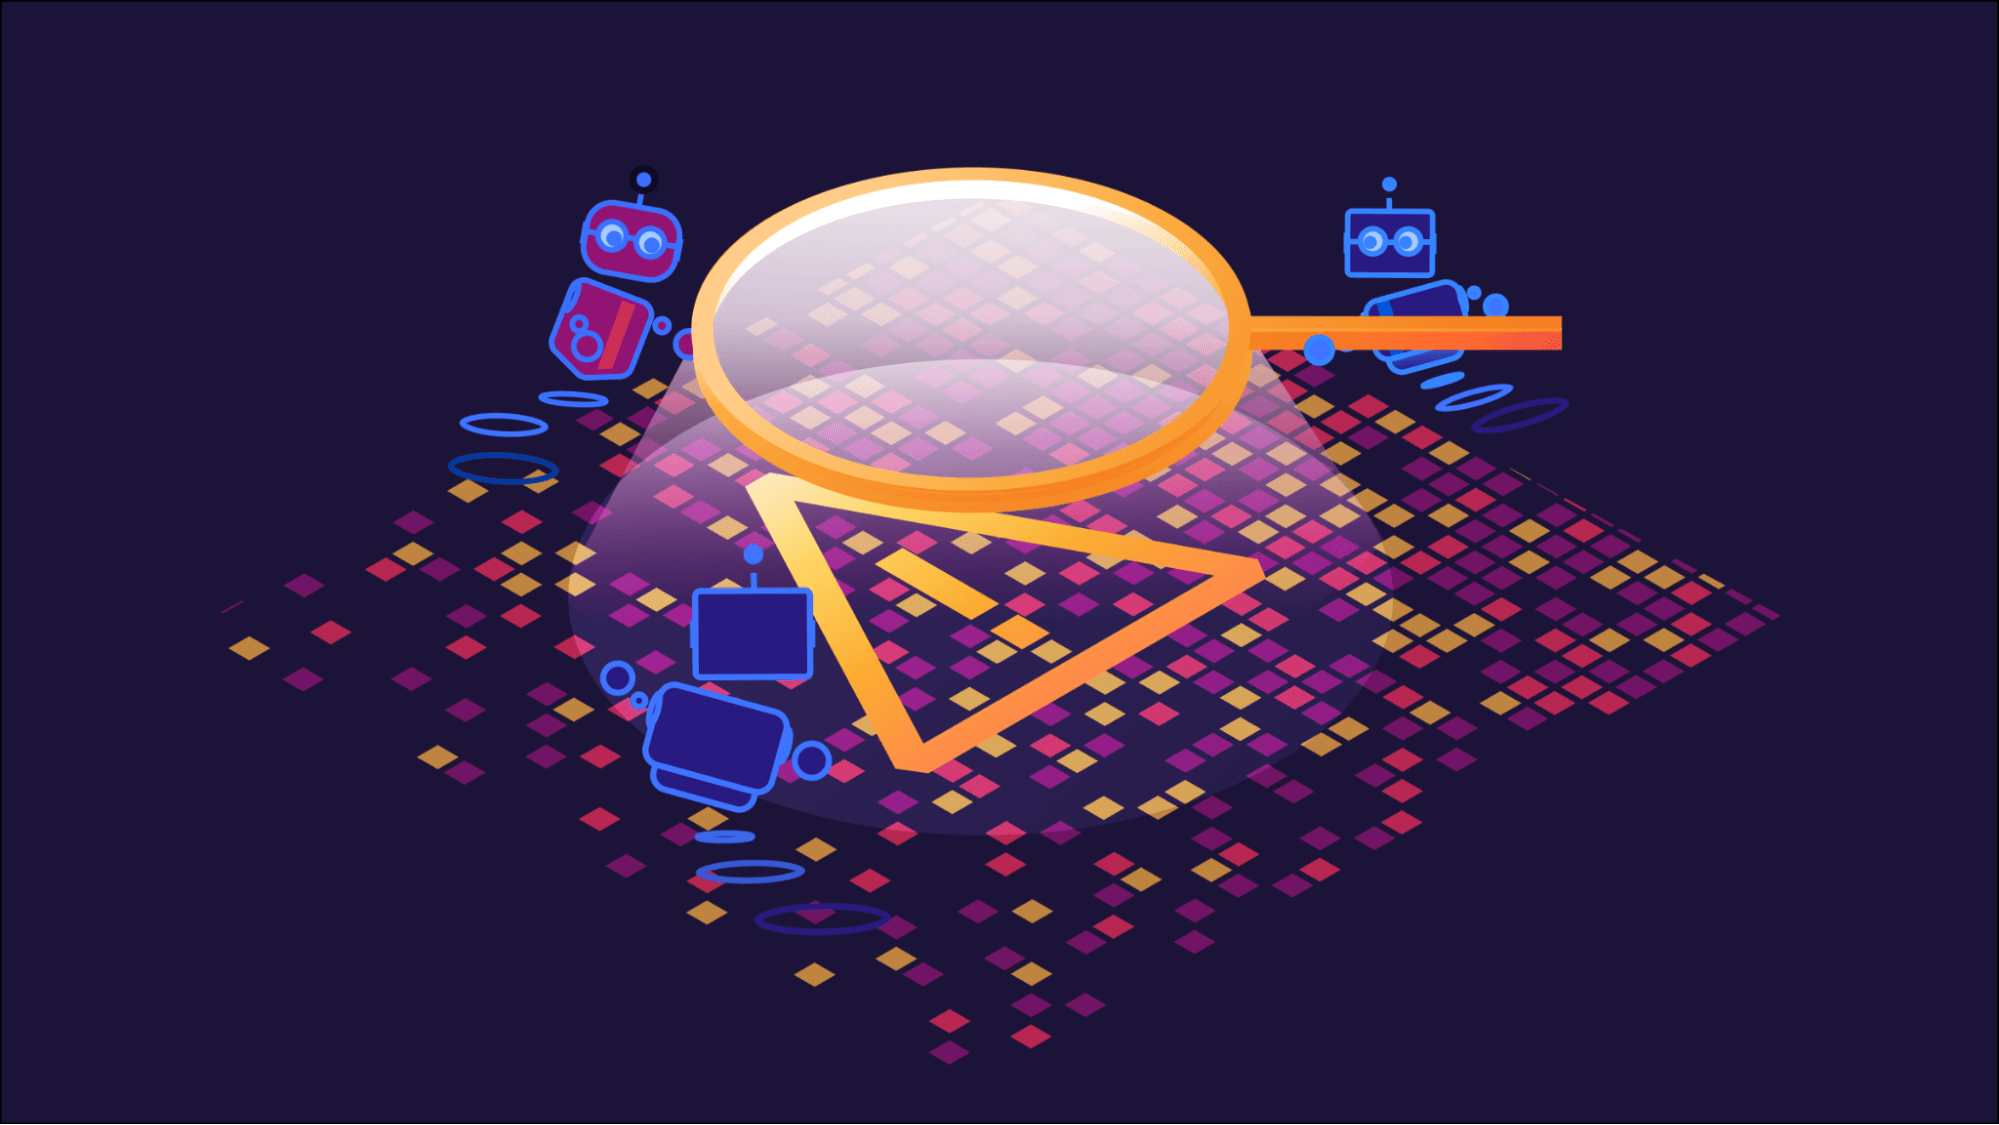
Cloudflare announced a multi-agent security operations system that processes security alerts far faster than human analysts. Built for the company's Managed Defense team, the system groups incoming alerts and surfaces related ones together.
How it works
The system runs in two stages: first, deterministic code executes fixed reconnaissance workflows to collect customer identity, detection history, traffic baseline, and network observations. Each data point is stored with its source, version, and timestamp. Then model-backed analysis kicks in.
For deeper analysis, Cloudflare uses the OpenAI Daybreak Defense Network and its partnership with Anthropic, leveraging approved GPT-5.6 Cyber and Mythos models. Initial analysis and scoring are handled by Clef, the company's open-source decision model.
Why a single agent fails
Cloudflare's first prototype showed that a single general-purpose agent could produce claims the evidence did not support. The company identified three recurring problems: context being treated as authority, scope drifting, and failed lookups losing the distinction between "not checked" and "checked and not found." As a result, evidence collection and scope enforcement were moved into application code before model analysis begins.