Full-stack security for agents
At GTC Berlin, NVIDIA announced the OpenShell Reference Architecture for building, containing, observing and enforcing safe AI agents on enterprise infrastructure and edge systems. The architecture builds on NVIDIA's OpenShell secure runtime software and aims to take agent development and operations to industrial scale.
What's inside
- Vera Rubin infrastructure: Runs inference for closed and open models. NVIDIA claims Vera Rubin NVL72 systems deliver 30x higher throughput per megawatt for agentic workloads.
- Vera CPUs: Operate agent harnesses and tool use; NVIDIA says they deliver 2x the performance of x86 processors.
- BlueField-4 DPUs: Run the NVIDIA Sentry security framework, continuously monitoring agent behavior. If an agent tries to move outside its software boundary, Sentry quarantines and stops it in milliseconds.
From edge to cloud
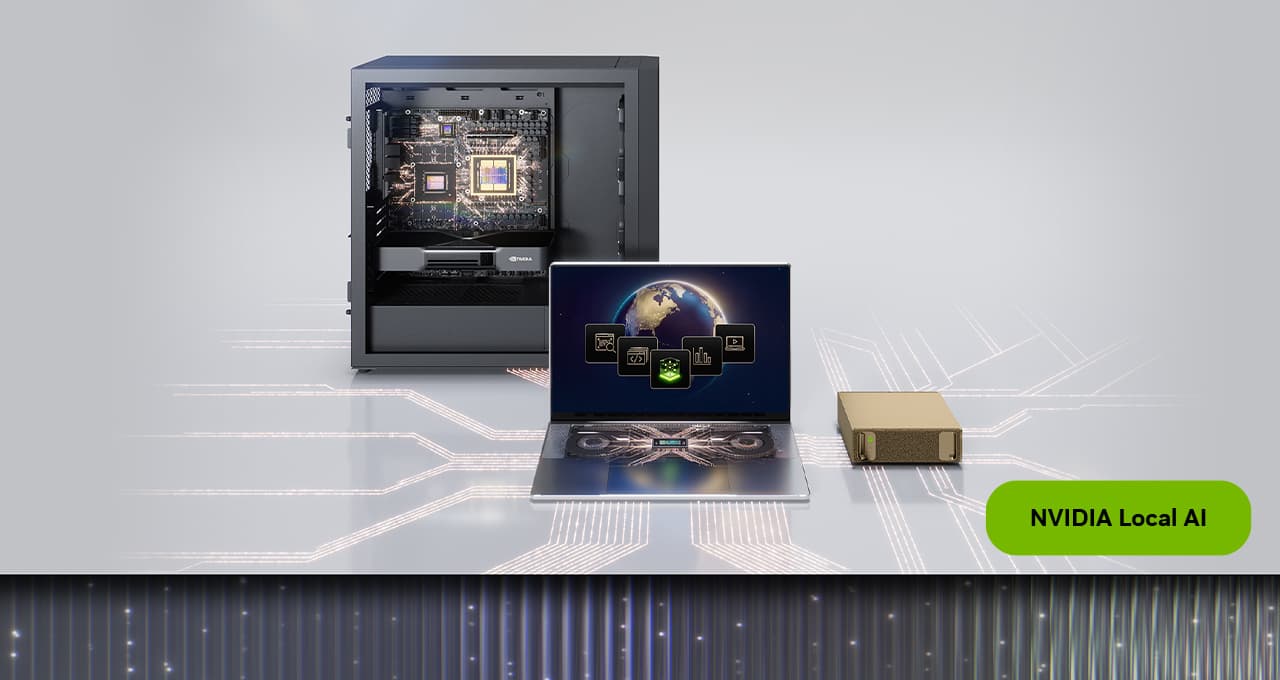
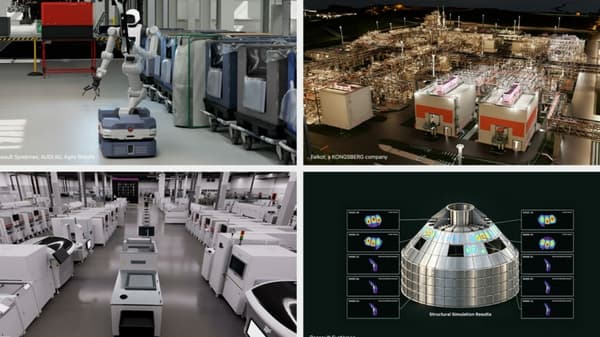
The architecture extends to the edge with RTX Spark, DGX Spark and DGX Station systems across industries such as retail, healthcare, manufacturing, robotics, software development and telecommunications. It runs on leading enterprise operating systems including Canonical, Red Hat, Microsoft Windows and Microsoft Execution Containers.
Broad partner ecosystem
Anthropic, AWS, Cisco, CrowdStrike, Dell Technologies, Google Cloud, HPE, IBM, Meta, Microsoft, OpenAI, Palo Alto Networks, Perplexity, SAP, ServiceNow and Siemens are among those working with the architecture to enhance the security of agent deployments. "AI capability and safety must advance together," said NVIDIA founder and CEO Jensen Huang, stressing that agents should have the freedom to do useful work within clearly defined boundaries.